Tag: Vulnerability Databases
-
How Much Lipstick Can That CVE Pig Wear?
Preface When I started writing this, I was still on the CVE editorial board, which I was removed from in 2018. That means I have been taking notes and working on this blog for over eight years. It’s a case of more and more evidence piling up and me not having time to pick a…
-
Q&A: Modernizing the National Vulnerability Database in the Age of Artificial Intelligence
The last two years of the National Vulnerability Database (NVD) has been tenuous, perfidious, and an outright disaster for organizations world-wide. That isn’t hyperbole unfortunately, as the program has continued to go downhill for more than two years. NVD is no longer a place to get usable vulnerability intelligence. It started back in 2024 at…
-
VDBs: Pedantic Nuances on Version Tracking
I am all about the pedantic nature of running a vulnerability database (VDB). It’s the backbone of running one well as “simply aggregating vulnerability information” is anything but simple. I’ve been outspoken on the issue of perceived simplicity for at least two decades and brought it up in various presentations and blogs. This blog is…
-
Noise2Signal Podcast: Which Does the Squirrel Bring?

For those not familiar, Mehul Revankar recently started a podcast named Noise2Signal. While there are a lot of podcasts out there and it is easy to lose track, this one stands out as Mehul has connections with a lot of folks that are significant in the history of information security. In fact, he interviewed Renaud…
-
What Do 2025 CVE Numbers Mean? An Intro.
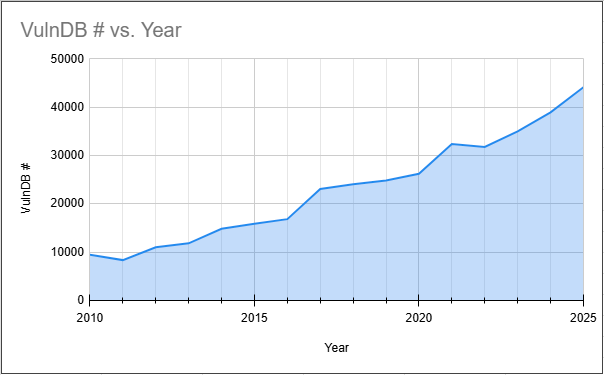
[This was originally my proposed introduction for Flashpoint’s 2026 Global Threat Intelligence Report. Due to the style of the report and covering a lot more intelligence sectors than vulnerabilities, only pieces of this were used. So I am publishing the entire original draft here for posterity.] The fact that there were over 48,000 CVEs published…
-
Bob’s “CVE Quality-by-Design Manifesto” – The Hit and Misses
Almost every time Bob Lord blogs, I feel the need to write a rebuttal to what is arguably abject stupidity and shortsightedness. One he published a couple days ago, titled “CVE Quality-by-Design Manifesto“, is missing several core concepts in the realm of vulnerability intelligence. While his overall point is certainly valid, the order in which…
-
Rest In Peace IBM X-Force Vulnerability Database
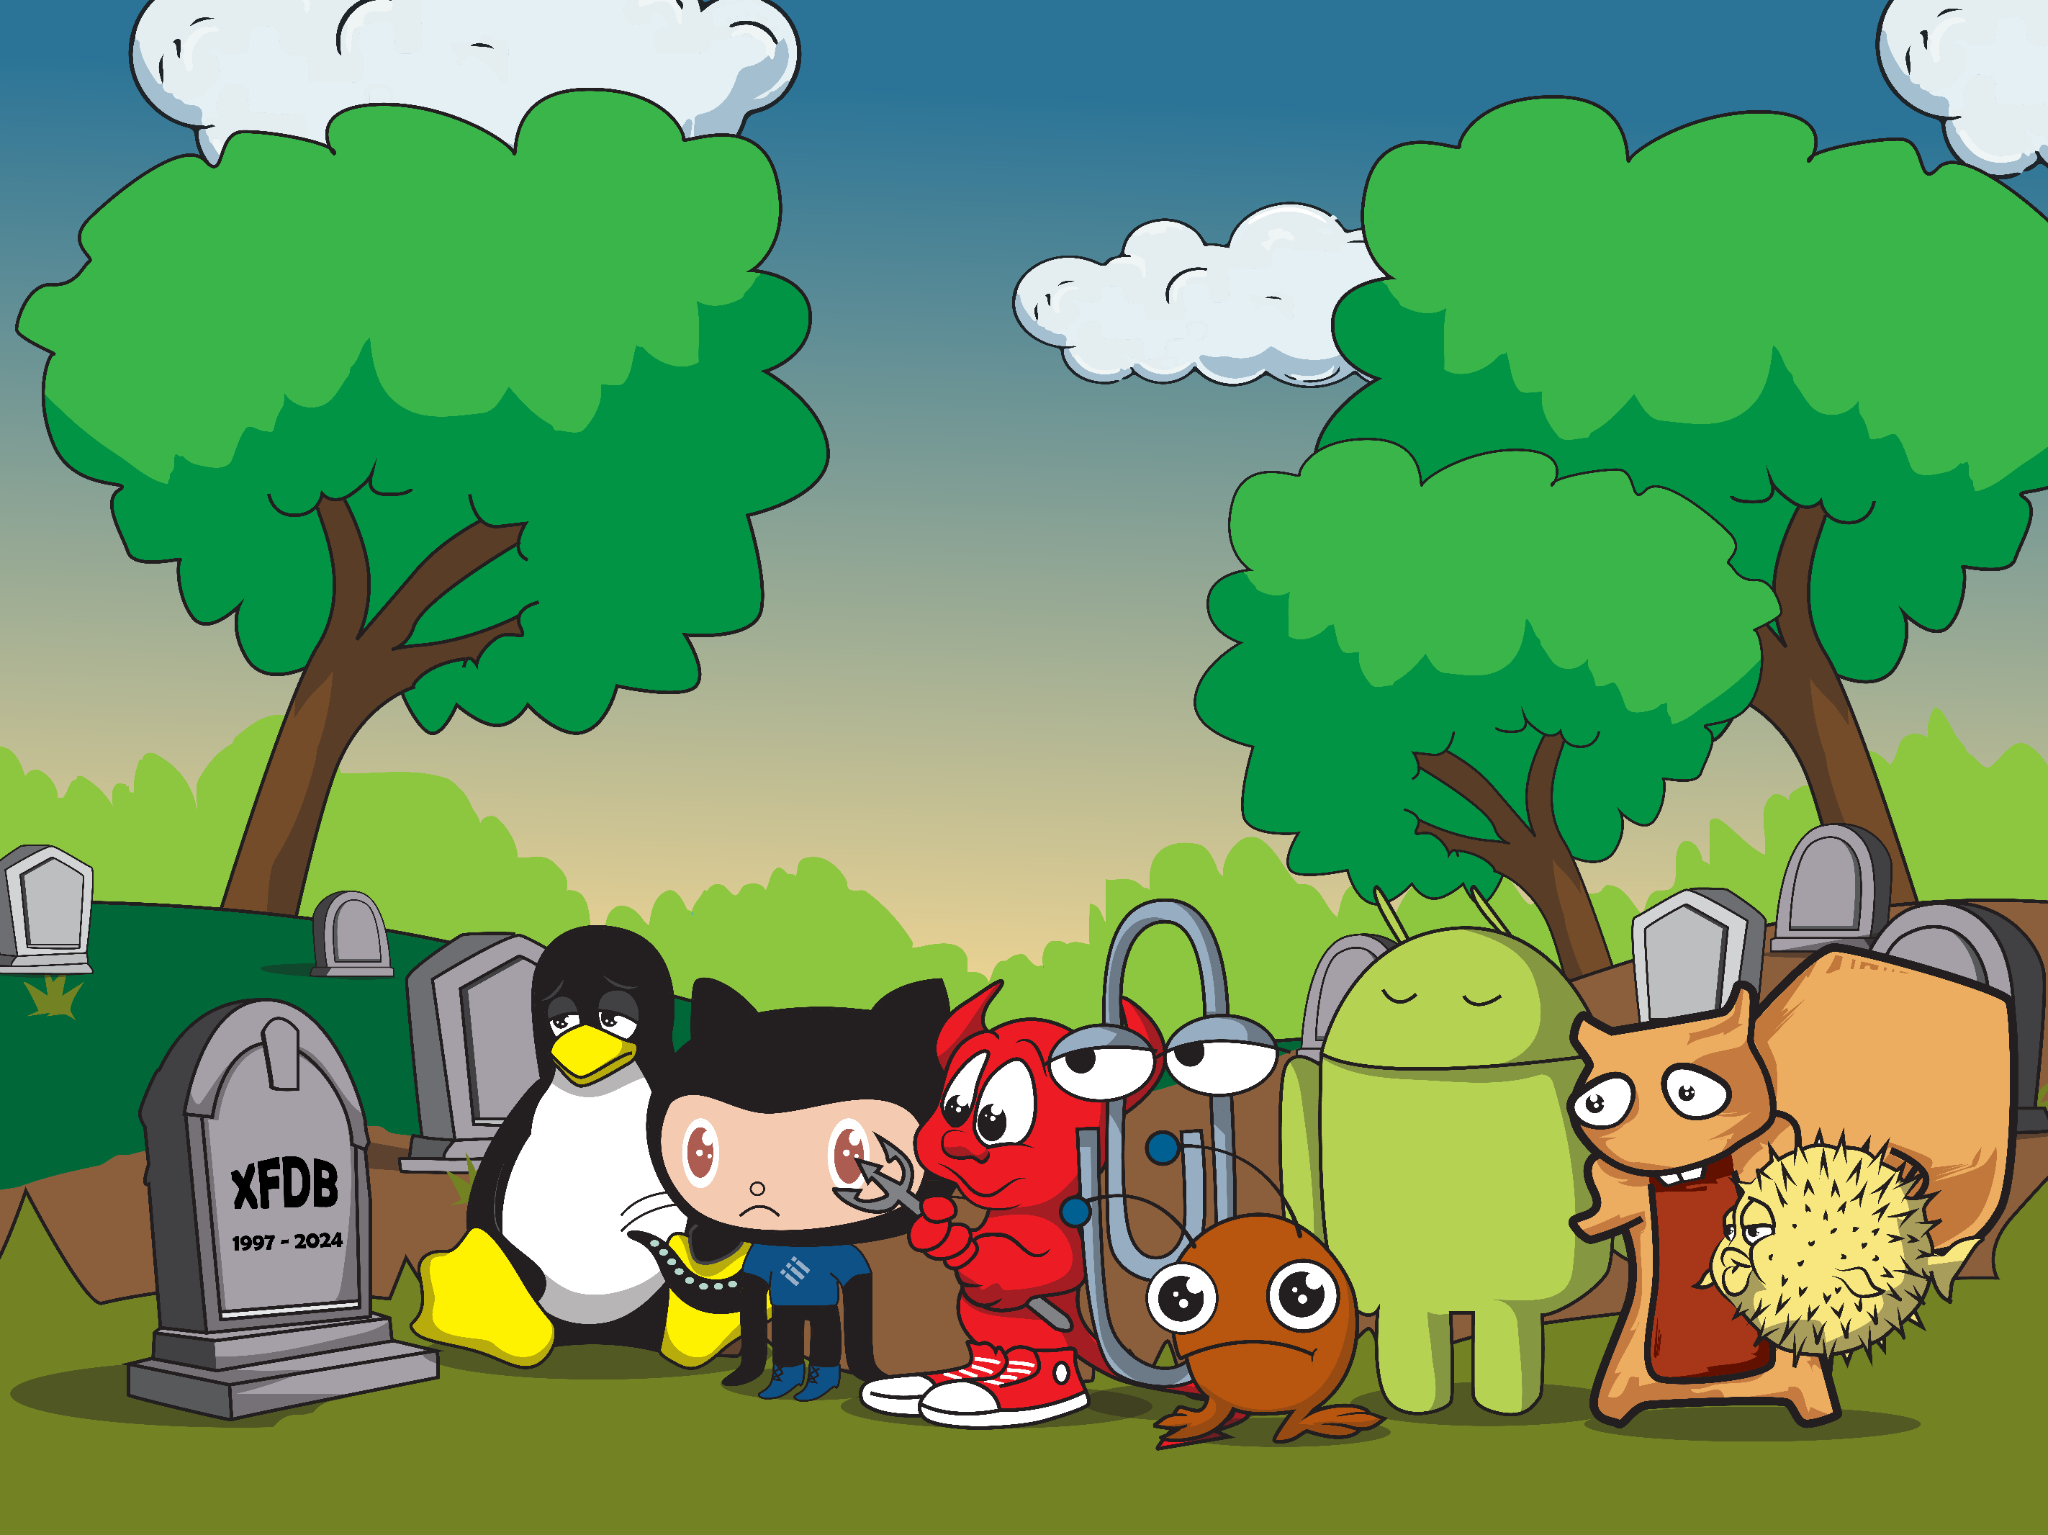
Within the vulnerability ecosystem, the CVE project / vulnerability database is certainly the most well-known. Over the past 30 years many others have come and gone, and others are still around. Some of you will recognize SecurityFocus BID, Open Sourced Vulnerability Database (OSVDB), Secunia, VulnDB, OSV, and others. Started in 1997, there is another that…
-
Reporting on the IBM 2025 Report

On April 16, 2025, IBM posted their X-Force 2025 Threat Intelligence Index. Like many reports of this nature, it covers a wide variety of aspects relating to threat intelligence. Of course, one of those aspects is vulnerability intelligence and this report has a section for that. You are reading this so you can guess where…
-
Who Reads Mega-advisories? No one! (Almost)

Vulnerability disclosure analysts are long familiar with so-called “mega advisories”, ones that typically come from vendors and often for products that ship appliances using hundreds of libraries or products with an entire operating system included. Such advisories can literally represent over 500 vulnerabilities in one shot. I’ll try to make this a bit fun! Disclaimer:…
-
CVE Farming – Problem & Solution

Blog Origins In the last year or two, I have increasingly used the term “CVE farming” in conversations and LinkedIn posts [1]. This has led a few people to ask what it meant and I gave a very cliff notes version of the answer. I started taking notes for this blog a while back expecting…