Tag: Vulnerability History
-
Noise2Signal Podcast: Which Does the Squirrel Bring?

For those not familiar, Mehul Revankar recently started a podcast named Noise2Signal. While there are a lot of podcasts out there and it is easy to lose track, this one stands out as Mehul has connections with a lot of folks that are significant in the history of information security. In fact, he interviewed Renaud…
-
What Was The “First” Vulnerability and…
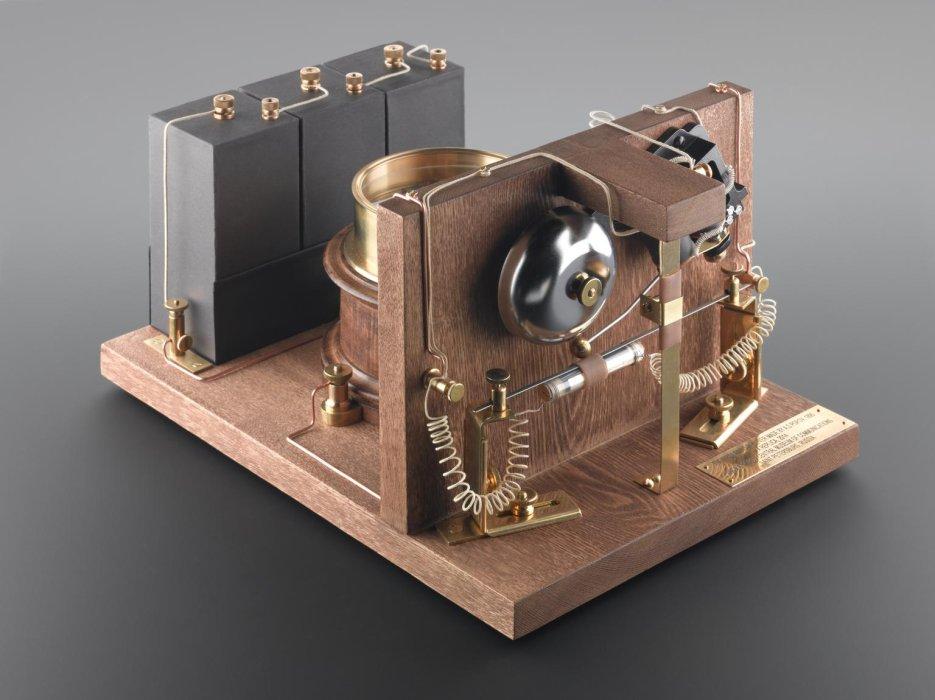
[This was originally posted to the Flashpoint blog, but underwent a fair number of edits. Curtis Kang also contributed to the blog, both original and was responsible for a lot of cleanup and making it more corporate. The version below was my first draft.] What is the first vulnerability? On first thought, it doesn’t seem…
-
Is the Kaseya Hack Actually a Supply Chain Attack?
[This was originally published on RiskBasedSecurity.com as part of a larger series on the Kaseya breach.] What is a Supply Chain Anyway? Within hours of the Kaseya breach becoming public, some critics called out that it was being incorrectly labelled as a supply chain attack. As Nick Carr pointed out, “precise language is important in…
-
The Value of Backfilling

[This was originally published on RiskBasedSecurity.com.] In every quarterly Vulnerability QuickView Report, we include a chart that shows how many vulnerabilities were disclosed so far that year, along with the most current counts of prior periods to show relative growth and decline. In some cases, like this year’s Q1, that chart shows a decline compared…
-
That Vulnerability is “Theoretical”!
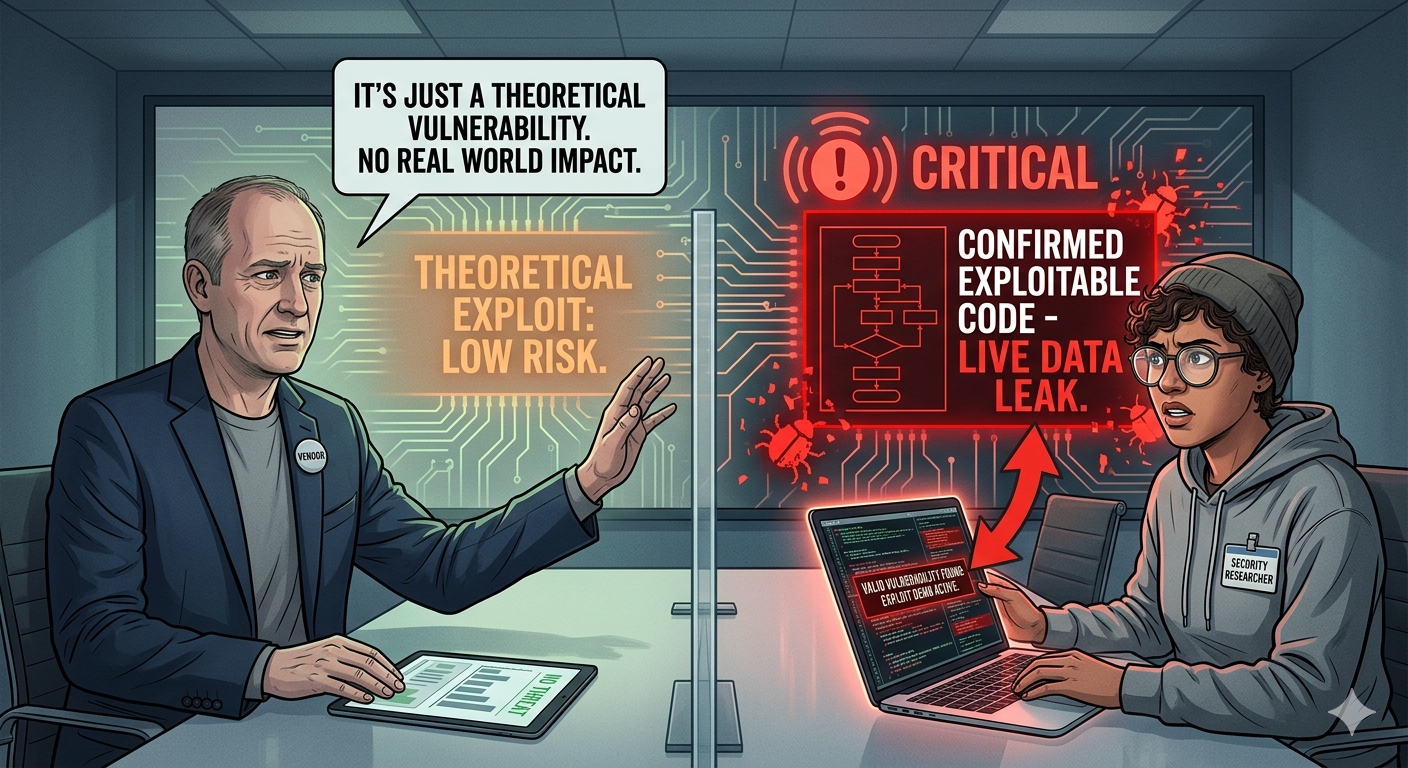
[This was originally published on the OSVDB blog.] A few days ago, while writing a draft of a different blog, I made reference to and said “we’re well aware of the pitfalls around calling a vulnerability ‘theoretical’“! I wanted to link off to what I was referencing, a case where security researchers found a vulnerability…
-
112 Years of Vulnerabilities: How did we get here, knowing what we know?
I gave a presentation on computer vulnerability history at BSides Delaware in November, 2013. Shortly after, I gave the presentation a couple times at Westchester Community College and the University of Pennsylvania, along with a brief version for the Invisible Harms conference at UPenn. The linked version is the revised copy after my initial run at BSidesDE. The talk gives a…