Tag: VulnDB
-
Case Study: Not A Vulnerability (NAV)

[This was originally published on RiskBasedSecurity.com in the 2018 Vulnerability Mid-year Report.] As stated earlier in this report, “incomplete information, constant updates and revisions, misinterpretation, and errors in reporting can all contribute to a level of confusion regarding the impact, severity and risk a vulnerability represents.” One way that this manifest is in vulnerability reports…
-
The Great (belated) Mozilla Firefox CVE Dump
[This was originally published on RiskBasedSecurity.com.] On June 11th, MITRE published descriptions and references for 318 entries, all relating to Mozilla Firefox. Yes; three hundred and eighteen entries. It may be tempting to think Mozilla was holding back on disclosures or there was a flurry of research activity leading to a slew of new vulnerabilities being discovered.…
-
Before you publish your end-of-year vulnerability statistics…

TL;DR – The CVE dataset does not allow you to determine how many vulnerabilities were disclosed in 2017. I’ll try to keep this fairly short and to the point, but who am I kidding? Every year for a decade or more, we see the same thing over and over: companies that do not track or…
-
Analysis Of The RANDom Report on Zero-days and Vulnerability Rediscovery

[This was originally published on RiskBasedSecurity.com.] On March 9, 2017, RAND released a report (PDF) titled “Zero Days, Thousands of Nights; The Life and Times of Zero-Day Vulnerabilities and Their Exploits” by Lillian Ablon and Andy Bogart that received a fair amount of press. The RAND press release goes on to describe it as “the first publicly available research to…
-
I do not think it means what you think it means… (CVE IDs)
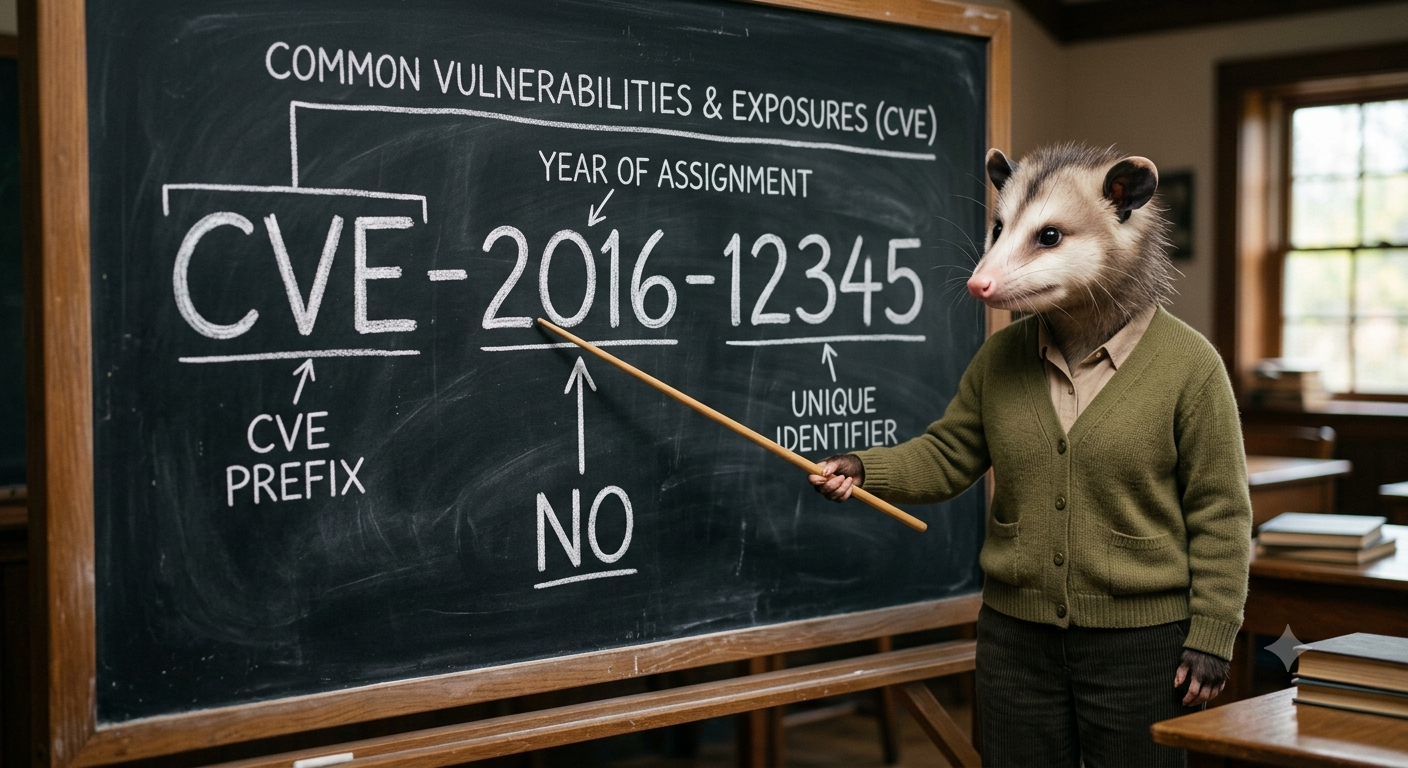
[This was originally published on the OSVDB blog.] Sometime in the past day or so, CVE-2016-10001 was publicly disclosed, and possibly a duplicate. Regardless, CVE-2016-10002 is also now public and legitimate. Tonight, I Tweeted that the presence of those IDs doesn’t mean what many will think it means. I say that based on the past…
-
Electronic Voting; an Old but Looming Threat

[This was originally published on RiskBasedSecurity.com.] As everyone on the planet knows, U.S. politics are in full swing with primaries almost every week and an upcoming presidential election in November of this year. At Risk Based Security we find it curious that one of the most dangerous topics seems to evade the 24-hour a day…
-
Our New Year Vulnerability “Trends” Prediction!
[This was originally published on RiskBasedSecurity.com.] Shortly after a year closes out, the industry is treated to dozens of security companies that want to tell you all about vulnerability totals and trends from the previous year. In many cases, the companies offering the predictions are armchair experts of a sorts, who do not aggregate vulnerability…