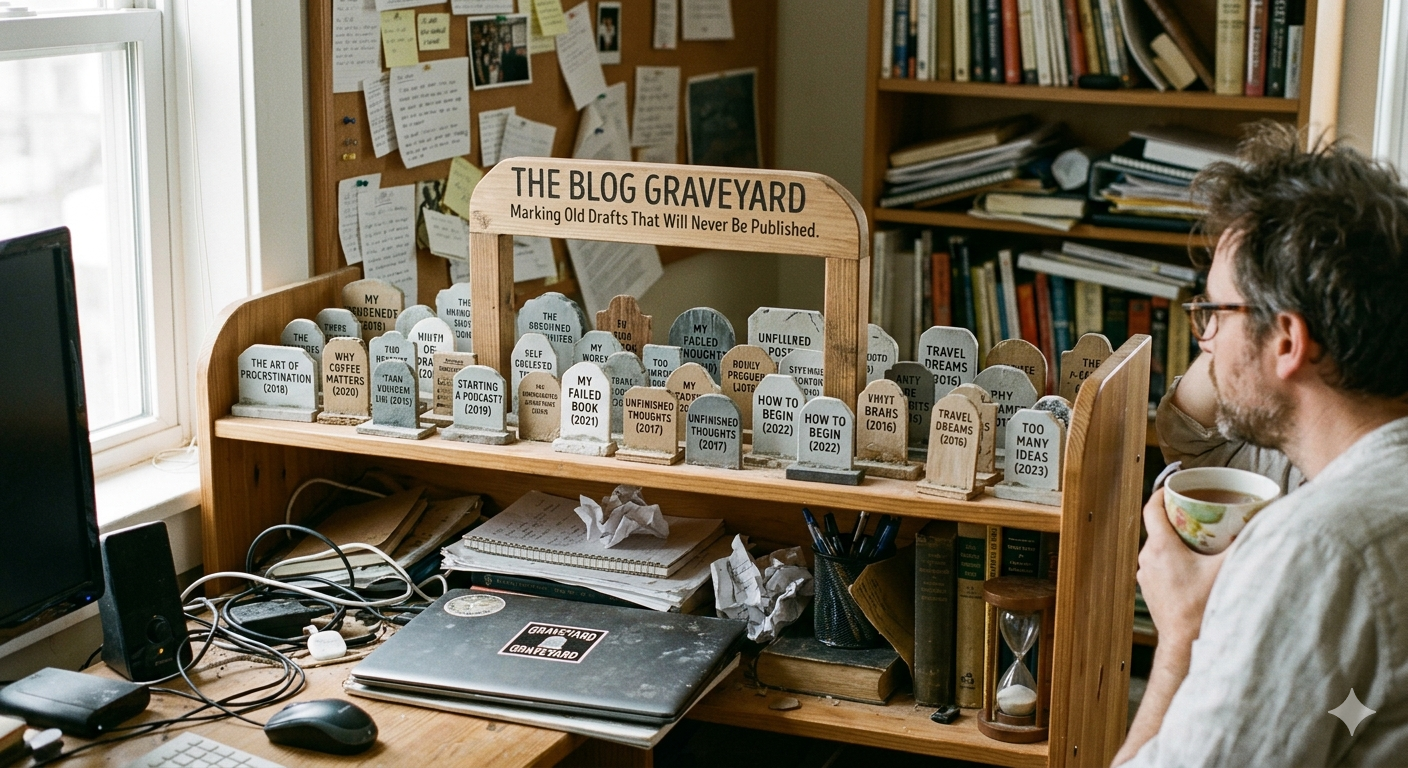
This is a continuing short run series of blogs summarizing old drafts and either declaring them dead, while listing them here, or keeping them as they are still relevant.
Part 1 – The Jericho Blog Graveyard (2010 – 2013)
Part 2 – The Jericho Blog Graveyard (2014 – 2015)
Part 3 – The Jericho Blog Graveyard (2016 – 2020)
Part 4 – The Jericho Blog Graveyard (2001 – 2013)
Part 5 – The Jericho Blog Graveyard (2014 – 2021).
See Part 5 about a flaw in my methodology that has the year ranges all over the place. =) For this graveyard we have:
- 2013 – A post about VUPEN, an old vulnerability intelligence service that published advisories riddled with problems, as well as heavily advertising their service. Much more so than is to be expected in an advisory. They also had a bad habit of not reporting the vulnerabilities to vendors.
- 2013 – Yet another blog started on the term “responsible” disclosure and how that needs to die.
- 2013 – A question on “Backdoors” was just loose notes about the concept and history of backdoors in products, what defines one vs ‘functionality’, etc.
- 2013 – Oracle and their lack of understanding CVSS or even the purpose of CVE. How they have a history of inaccurate scoring, inaccurate metadata around a vulnerability (e.g. local vs remote), and more. This is fairly well known to the people that work with vulnerability disclosures.
- 2013 – Bug Bounties – Was to be a huge exposition examining bug bounty programs, current views, and interesting observations.
- 2014 – A blog pointing out amusing changelog entries. Would have been a fun one but I didn’t stay diligent on documenting them as I saw them.
- 2015 – “Disconnect”, about that and a comparison between engineering and computer sciences / InfoSec. It isn’t a good juxtaposition for many reasons and a lot of the “real world” analogies are wrong.
- 2015 – Security Incident Counting Crap – as an industry, we’re not good at actually counting things like breach incidents, introducing too much bias for it to be useful often times.
- 2015 – Reality of CFP and Researcher Ethics – A look at how many presentations to conferences like DEF CON and Black Hat Briefings are missing ethical considerations, as well as how much garbage is accepted as a talk.
- 2021 – On the topic of blue vs red team, and how some skills do not translate from one to the other like many think.
- 2021 – Fitbit – Was to be a tear-down of all the flaws and issues with a couple Fitbit models.
- 2021 – CNVD Behind the Scenes? – On the back of a report from a threat intel vendor on CNVD vs NVD comparison, I had a couple dozen examples of CNVD entries and how they were somewhere between lacking and unusable. You can’t just count volume when comparing the two databases.
- 2021 – Exploit Trolling, The Other Side – Citing examples of, at the time, increasing examples of people publishing “exploits” for high profile vulnerabilities that were actually not. Some were a lesson to researchers and printed harmless “I could have rm’d your drive” type messages, others considerably more malicious.
- 2021 – Resisting the Digital Census – Thoughts about security professional quotes about “everyone is already owned” but pointing out missing bits of the thought process that got them there. Basically how threat actors operate versus the hyperbole found in said quotes.
Leave a Reply