Tag: CVE
-
WhiteSource on ‘Open Source Vulnerability Databases’ – Errata

[This was originally published on the OSVDB blog.] On September 8, 2016, Jason Levy of WhiteSource Software published a blog titled “Open Source Vulnerability Database”. Almost two years later it came across my radar and I asked via Twitter if WhiteSource was interested in getting feedback on the blog, since it contained errata. They never…
-
CVE and the matter of “unique” ID numbers

Common Vulnerability Enumeration, now known as Common Vulnerabilities and Exposures (CVE) is a vulnerability database (ignore their silly claim to be a ‘dictionary’) that the information security industry relies on heavily, unfortunately. Per MITRE’s CVE page, “CVE® is a list of entries—each containing an identification number, a description, and at least one public reference—for publicly…
-
Microsoft, CVE, MITRE, ETERNALBLUE, Headache…

2019-02-14 Update: Thanks to Chris Mills @ MSRC (@TheChrisAM), who has been working behind the scenes since this blog was published, he has brought clarity to these assignments! MSRC is still potentially touching up some additional documentation to make it easier to see these associations, but here is the definitive answer from him: CVE-2017-0143 ShadowBrokers…
-
Case Study: Third-Party Plugins

[This was originally published on RiskBasedSecurity.com in the 2018 Q3 Vulnerability QuickView Report.] Many people are familiar with content management systems (CMS), which are used in a variety of roles. Millions of people use them via hosted software such as WordPress.com and companies use them for blogging and knowledgebase systems. Historically, despite their wide deployment,…
-
Our Reports Clickbait? No. Click Here To Find Out Why…
[This was originally posted to the Risk Based Security blog (now 404 and no IA copy), with contributions from Jake Kouns.] Last week, we published our 2018 mid-year report that included an overview of the vulnerabilities that we have tracked and included in VulnDB. We highlighted a key takeaway from the report in the title:…
-
Case Study: Not A Vulnerability (NAV)

[This was originally published on RiskBasedSecurity.com in the 2018 Vulnerability Mid-year Report.] As stated earlier in this report, “incomplete information, constant updates and revisions, misinterpretation, and errors in reporting can all contribute to a level of confusion regarding the impact, severity and risk a vulnerability represents.” One way that this manifest is in vulnerability reports…
-
The Great (belated) Mozilla Firefox CVE Dump
[This was originally published on RiskBasedSecurity.com.] On June 11th, MITRE published descriptions and references for 318 entries, all relating to Mozilla Firefox. Yes; three hundred and eighteen entries. It may be tempting to think Mozilla was holding back on disclosures or there was a flurry of research activity leading to a slew of new vulnerabilities being discovered.…
-
Thoughts about CNNVD vs. US NVD

[This was originally published on RiskBasedSecurity.com in the 2017 Q3 Vulnerability QuickView report.] In October, Bill Ladd of Recorded Future released a study comparing CVE and the U.S. NationalVulnerability Database (NVD) with China’s National Vulnerability Database (CNNVD). This report, titled“The Dragon Is Winning: U.S. Lags Behind Chinese Vulnerability Reporting” was covered by John Leyden inThe…
-
2017 End-of-year Reports Based on CVE Data

[These were notes I took in 2017 and never got around to finishing. I have done some general formatting / cleanup to round out the sentences and such, but not much else. Given I made a prediction at the time, I am opting to publish this but backdate is accordingly. The general issue of CVE…
-
I do not think it means what you think it means… (CVE IDs)
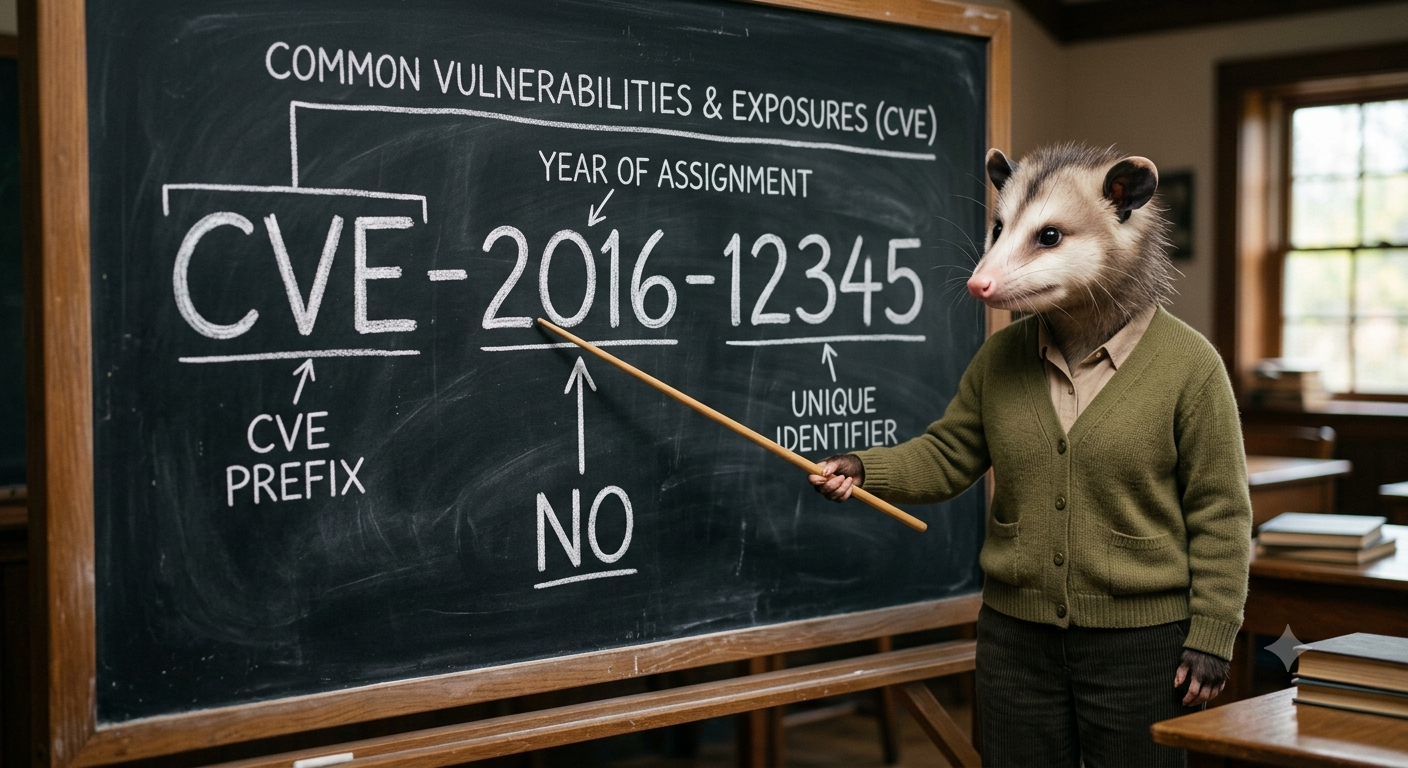
[This was originally published on the OSVDB blog.] Sometime in the past day or so, CVE-2016-10001 was publicly disclosed, and possibly a duplicate. Regardless, CVE-2016-10002 is also now public and legitimate. Tonight, I Tweeted that the presence of those IDs doesn’t mean what many will think it means. I say that based on the past…