Tag: Vulnerability Disclosure
-
Don’t Be a CVE Dummy

One of the aspects of vulnerability intelligence is monitoring various public sources for new vulnerabilities, especially ones with a Common Vulnerabilities and Exposures (CVE) ID. These numbers are designed to help communicate details about a specific vulnerability. “Hey, remember that remote code execution in Fortinet in May?” Unfortunately, that isn’t very specific as there were…
-
Vulnerability Forecasting Technical Colloquium – A Few Thoughts

[I wrote this on September 21st, but apparently forgot to ultimately move from GDoc to Blog. I suspect because it really needs to be cleaned up as it is my first draft. Rather than do that, since the event has passed, I will just backdate instead. This blog was actually published December 28, 2024.] Part…
-
The Linux CNA – Red Flags Since 2022

[2/28/2024 Update: A bit more info added at end regarding “almost any bug might exploitable“.] MITRE announced that The Linux Kernel Organization (Kernel.org, hereafter referred to as ‘Linux’) was officially a CVE Numbering Authority (CNA) on February 13, 2024 and via the CVE web site, that their advisories would be posted here. That means they…
-
No one will burn a zero day on you…?

For at least two decades, a common mantra in the Information Security industry is that “no one will burn a zero day on you!” This is typically said to a person, often someone that comes across as overly paranoid, or perhaps a small hobby website. This term refers to zero day vulnerabilities, ones that are…
-
That Vulnerability is “Trending” … a Redux

A couple weeks ago I published a blog titled “That Vulnerability is ‘Trending’ … So What?“. I didn’t think I would be publishing another on this topic, especially this fast. But I ran into another absurd case of a vulnerability “trending” and figured out why, which is even more ridiculous. I caused this… A CVE…
-
That Vulnerability is “Trending” … So What?

Yesterday, more than one organization reached out to my company asking why a particular vulnerability wasn’t in VulnDB yet. First, it had been less than 24 hours since publication in CVE/NVD, NVD hasn’t analyzed it as of the time of this blog, and it is in software no significant business would use. It’s part of…
-
Rebuttal? Not really… Comments on Curphey’s Latest Blog
I went into a LinkedIn post expecting to have to buy a new box of red sharpies to be honest, but I am pleasantly surprised at the conclusions regarding CVE / NVD, which I think are largely accurate. As grim a picture as is painted, they are still a bit too generous. I say that…
-
What Was The “First” Vulnerability and…
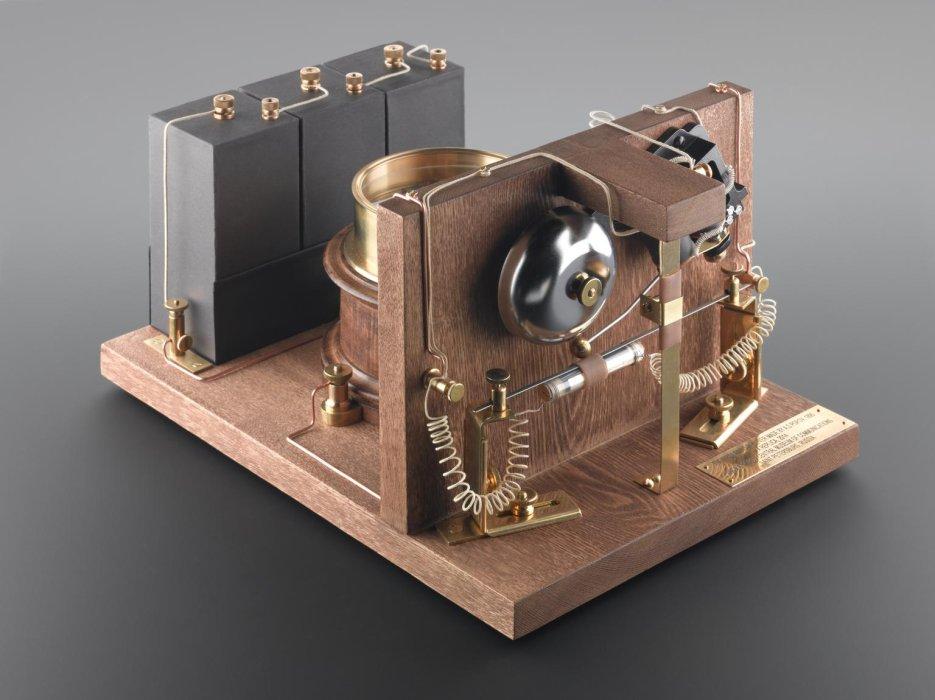
[This was originally posted to the Flashpoint blog, but underwent a fair number of edits. Curtis Kang also contributed to the blog, both original and was responsible for a lot of cleanup and making it more corporate. The version below was my first draft.] What is the first vulnerability? On first thought, it doesn’t seem…
-
Let’s Talk About 0-days

[This was a first draft of an article to be published on the Flashpoint Threat Intel blog. Ultimately, parts of it were adopted for a different blog but the original remains considerably different. Curtis Kang contributed significantly to the finished blog below.] Zero-days (0-days and other variations) are exploitable vulnerabilities that the general public is…
-
Rebuttal: Skeletons in the Closet
On April 22, 2022, Nate Warfield of Prevailion published an article on Threatpost on the topic of zero days. I’m a little late to this article, but because this horse still has some life in it apparently, I feel obligated to once again point out how the term ‘zero day’ has basically lost all meaning.…